Imagine it is graduation day.
The gown fits. The photographer is ready. Your parents are smiling as though they personally wrote your final-year project. Your friends are busy calculating how many years of suffering the degree represents, and someone has already posted, “Next stop: CEO!”
Then you receive a message asking you to update your online account.
You hesitate. You have just survived assignments, examinations, tuition deadlines and the mysterious disappearance of marks from a portal. Surely, the internet cannot have another problem for you.
Unfortunately, the internet does not recognise graduation dates.
It does not care whether you are a first-year student still confusing lecture rooms, a student who knows every shortcut on campus, a graduand waiting for a gown, or an alumnus who has not visited Bugema since collecting a transcript.
If you use digital systems, you are part of the story.
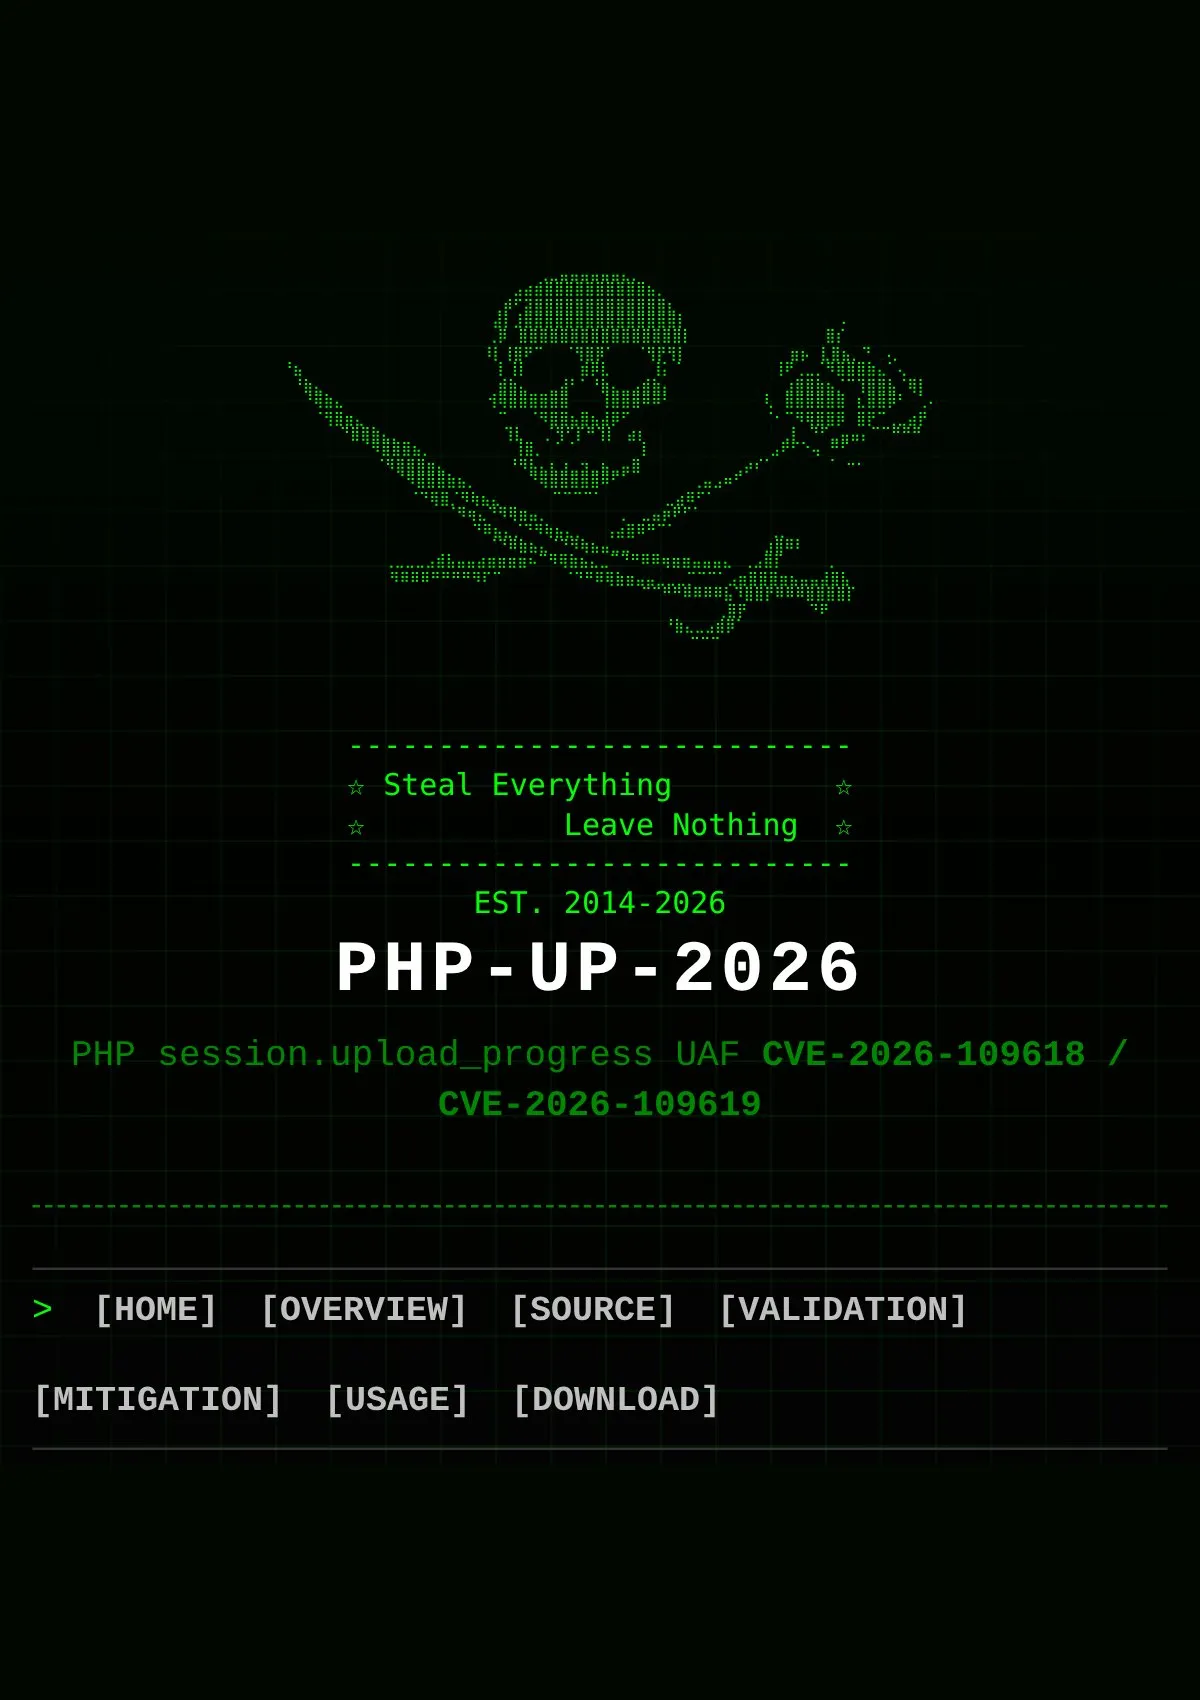
And this week, the story has a rather uncomfortable name: PHP2Shell.
The Internet Has a Problem. No, It Is Not Your Wi-Fi.
On 21 October 2026, the PHP development team released emergency security updates addressing two critical vulnerabilities identified as CVE-2026-109618 and CVE-2026-109619. Both received a severity rating of 9.2 out of 10 under the CVSS v4.0 system. Security researchers collectively refer to the vulnerabilities as PHP2Shell.
In ordinary language, these flaws could allow an attacker to exploit certain vulnerable PHP server configurations without first logging in, potentially executing unauthorised code, exposing information or disrupting services. The exact risk depends on the software version and server configuration.
This does not mean every website has been hacked. It does not mean every university has lost its records. And it certainly does not mean your GPA has suddenly become public property.
It means a serious weakness was discovered in widely used software, security updates were released, and administrators needed to act quickly.
That is serious enough without adding fictional drama.
So, What Exactly Is PHP?
Think of a website as a restaurant.
The page you see on your phone is the dining area. The server is the kitchen. The database is the store where ingredients and records are kept. PHP is one of the technologies that can help process an order behind the scenes.
When you log in, search for information or request a page, the server may use PHP to process the request, communicate with a database and return the information your browser displays.
PHP is used across a substantial part of the web, including many websites and content management systems. That broad presence is one reason a serious flaw in the PHP runtime deserves international attention.
Now imagine discovering that, under certain conditions, a specially crafted request can exploit a weakness in the kitchen's machinery.
The problem is no longer whether the waiter knows your name. The problem is whether the kitchen itself is operating securely.
That is the uncomfortable part of PHP2Shell.
The weakness is in the underlying PHP software, rather than simply in one poorly written website. Consequently, changing a website's colours, updating a plugin or telling users to choose stronger passwords does not, by itself, fix the underlying PHP vulnerability. The affected PHP installation must be appropriately patched.
In cybersecurity, sometimes the problem is not the person knocking at the door. It is the lock.
The Hacker Does Not Need a Student ID
At university, access to certain places requires identification, authorisation or permission. You cannot simply walk into every office, open every cabinet and announce that you are conducting research.
Computer systems also have access controls, but security weaknesses can undermine them.
Certain vulnerabilities allow attackers to bypass the normal route into a system by exploiting how the software itself handles incoming requests. In the case of PHP2Shell, successful exploitation could potentially allow remote code execution, meaning an attacker could cause a vulnerable server to execute unauthorised commands.
Imagine asking a computer to perform an ordinary task and discovering that someone has found a way to make it perform a completely different one.
That is not magic. It is a software security failure.
And unlike the student who arrives late for a lecture and quietly enters through the back door, an attacker exploiting a server vulnerability may never physically visit the institution.
No visitor's book. No gate pass. No security guard asking, “Oli wa?”
Just network traffic.
To be clear, exploiting these flaws is not guaranteed to succeed against every PHP website. The particular server setup, installed version, privileges and other protective measures all matter. But the possibility of unauthorised code execution is precisely why the vulnerabilities received such urgent attention.
The Most Dangerous Sentence in IT: “It Has Always Worked.”
There is a peculiar habit in technology: when a system works consistently, people begin to assume it will continue working forever.
A website has been running for five years, so nobody checks its software version. An application still opens, so nobody asks whether its dependencies are supported. The server has not crashed, so everyone assumes it is healthy.
Then a security advisory appears, and suddenly that old server becomes the most interesting machine in the building.
The truth is that working software is not necessarily secure software.
A system can load pages perfectly while running outdated software. It can display the correct information while carrying an unpatched vulnerability. It can look professional on the outside while needing urgent attention underneath.
That is why security maintenance includes more than fixing visible problems. Administrators must inventory their systems, track software versions, apply vendor updates, monitor suspicious activity and verify that their security controls are functioning.
In other words, an IT department should not wait for a website to fall sick before checking whether it has been exposed to a known threat.
Prevention is less dramatic than recovery, but usually far more desirable.
AI Helped Find the Problem. Technology Is Both the Detective and the Crime Scene.
One of the intriguing dimensions of the PHP2Shell story is the role of artificial intelligence-assisted research in identifying the vulnerabilities.
AI and advanced security research tools can help investigators analyse code, identify suspicious behaviour and investigate complex software weaknesses. Such capabilities can improve the speed at which researchers discover problems.
But there is a paradox here.
The same technological progress that helps people build sophisticated systems can also help researchers discover weaknesses in those systems. And as security tools become more powerful, both defenders and attackers may seek to use them.
That does not mean AI is inherently dangerous or that every vulnerability is discovered by artificial intelligence. It means the security landscape is changing, and organisations need people who understand both the opportunities and the risks of emerging technology.
For software engineering students, this should be a wake-up call.
Learning to build an application is important. Learning how to secure it, maintain it, test it and respond when something goes wrong is equally important.
A developer who can create a beautiful login page has accomplished something useful.
A developer who also understands authentication, authorisation, secure coding, dependency management, logging, patching and incident response is preparing for the real world.
The future does not need people who can merely make computers do things.
It needs people who understand what computers should never be allowed to do.
Because you may graduate from university, leave the campus gates behind and change your career three times, but you never graduate from the responsibility of staying digitally safe.